Scan Dependency Vulnerabilities
The built-in Osv Source Scanner scans dependency manifests and lock files, publishes a vulnerability report, and fails the build when findings reach your chosen severity threshold.
Prerequisites
Use an active Enterprise subscription and a Docker-capable executor. Check Administration / Subscription Management first. Without an active subscription, the step stops at check-subscription before scanning. The executor also needs network access to pull the scanner image and query public dependency and vulnerability services.
Create a scan job
In a disposable project, create backend/requirements.txt containing deliberately old dependencies:
requests==2.19.1
Django==2.2.0
These versions are a scan fixture, not dependencies to use in an application. The job scans the manifest without running an application built from it.
Add this .onedev-buildspec.yml, commit it, and run Scan Dependencies:
version: 53
jobs:
- name: Scan Dependencies
  steps:
  - !CheckoutStep
    name: Checkout code
    cloneCredential: !DefaultCredential {}
    withLfs: false
    withSubmodules: false
    condition: SUCCESSFUL
  - !OsvSourceScannerStep
    name: Scan dependencies
    scanPaths: backend
    reportName: Vulnerabilities
    recursive: true
    failThreshold: HIGH
    publishJSONReportAsArtifact: true
    condition: SUCCESSFUL
  retryCondition: never
  timeout: 600
The checkout step is required: the scanner reads files in the job working directory. Scan Paths limits this example to backend; leave it empty to scan the working directory. Enable Recursive when manifests are nested below that location.
Read the result
Open the build's Vulnerabilities tab. Findings show their severity, dependency version, advisory details, and available fixed versions. Counts and recommendations change as vulnerability databases are updated.
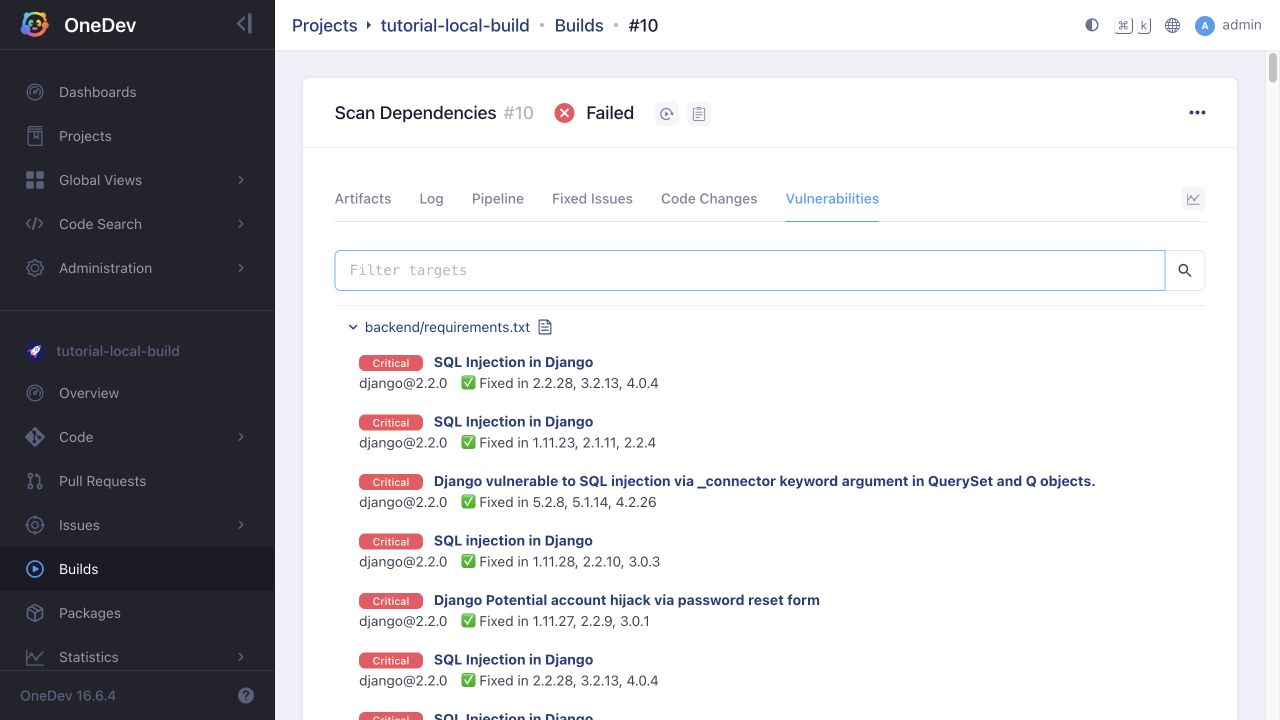
With Fail Threshold set to High, High and Critical findings fail the report-publishing step. This is an expected policy failure, distinct from a scanner execution or network error. The report is still available. Publish JSON Report As Artifact also preserves .osv-scanner-vulners.json under Artifacts, including when the severity threshold fails.
Update your application's dependencies and lock files, test compatibility, and scan again. For a small independent control, replacing the fixture with six==1.17.0 produced a passing scan during this tutorial's verification. A passing result means no reported finding reached the threshold at scan time; it does not guarantee the absence of vulnerabilities.
Automate scanning
In the job's Params & Triggers, add a Branch Update trigger for the manifest and lock-file paths used by your project. Also add a Schedule trigger, for example daily at 01:00, so newly published advisories are checked even when your repository has not changed. Select the branches you intend to scan.
In More Settings, a notification post-build action can notify the responsible users when a build fails after a successful build. Configure the server's mail service and recipients before relying on email delivery.
You can also make this job a dependency of deployment jobs or require it in branch protection. Report visibility follows the job/report permissions assigned to the viewer. An OSV configuration file can suppress selected findings when justified, but suppression does not fix a vulnerable dependency.