Insecure Docker Registry
Docker image pulls and pushes use the Docker daemon, while the Build Image step uses a BuildKit builder. Configure the component that contacts your registry on every server or agent that can execute the job. A daemon setting alone does not configure a docker-container BuildKit builder.
Configure Docker Daemon
On Linux, merge the following entry into /etc/docker/daemon.json, preserving existing settings:
{
    "insecure-registries": ["<registry host>:<registry port>"]
}
Restart Docker during an appropriate maintenance window, for example with sudo systemctl restart docker on a systemd installation. On Docker Desktop, merge the entry in Settings → Docker Engine, then apply and restart.
Use the registry host and port without a URL scheme or project path. Verify with docker info, then try docker login and docker pull against that registry.
Configure Docker Builder
In Administration → Job Executors, edit the Docker executor and expand More Settings. The Buildx Builder field selects the builder; the default is onedev, including for auto-discovered executors.
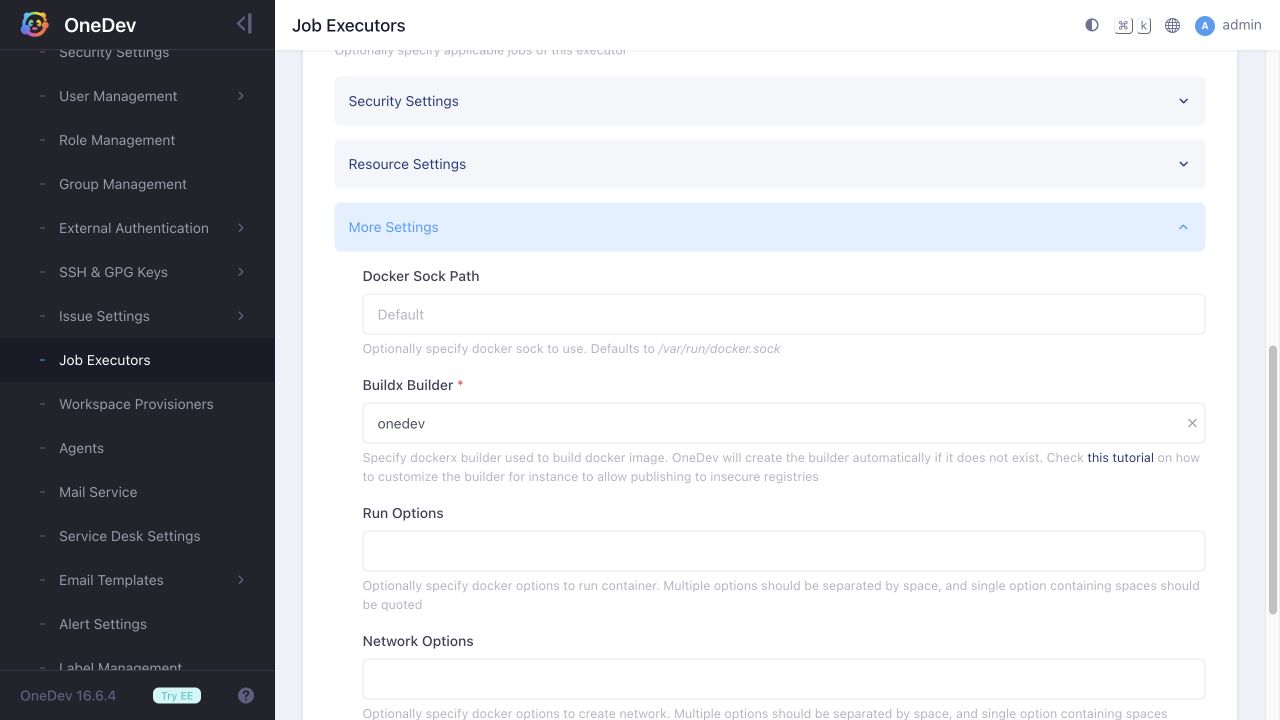
Create a dedicated builder to avoid removing an existing builder or its cache:
-
Create
/etc/buildkit/buildkitd.toml(or another readable file). For a plain HTTP registry, use:[registry."<registry host>:<registry port>"]http = trueFor HTTPS with an untrusted self-signed certificate, use
insecure = trueinstead ofhttp = true. Prefer configuring the registry's CA certificate when available. -
Run the following as the OS user whose Docker client runs the job, against the same Docker daemon used by the executor:
docker buildx create --name onedev-local-registry \--driver docker-container \--buildkitd-config /etc/buildkit/buildkitd.tomldocker buildx inspect onedev-local-registry --bootstrap -
Set the executor's Buildx Builder to
onedev-local-registryand save. Create the same named builder on each eligible agent host for a remote Docker executor. Set Applicable Jobs appropriately if this executor is intended only for selected projects or jobs. -
If OneDev or its agent runs in a container, the Docker client inside that container must be able to see the builder configuration. Mount the host user's Buildx directory into the container user's home, for example:
-v <user home>/.docker/buildx:/root/.docker/buildxAdd this to your existing server or agent container configuration along with its Docker socket mount.
-
Run a Build Image step with registry output and the appropriate Registry Logins. Check that the published image can be pulled and that its package page identifies the publishing build.
The registry hostname must resolve and be reachable from both the Docker daemon and the BuildKit container. For OneDev's built-in registry, configure Server URL with that reachable address; container-local localhost is generally unsuitable.